

Does the Binance Security Incident Put Your Ethereum Wallet at Risk? EIP-7702 and Wallet Delegation Explained
The Binance security incident on October 30, 2026 has pushed a relatively technical Ethereum feature into a much broader security discussion: EIP-7702 wallet delegation.
For ordinary Ethereum users, however, the most important question is not whether EIP-7702 appeared somewhere in the incident timeline. It is whether the same class of authorization risk could affect a personal wallet holding ETH, USDT, USDC or other Ethereum assets.
The short answer is that the Binance incident does not mean ordinary Ethereum wallets are automatically at risk. Binance’s preliminary investigation points to a compromised DevOps engineer’s laptop that allowed an attacker to access a service container and submit unauthorized withdrawal transactions. Binance said it had found no evidence that wallet private keys were leaked and estimated the total impact at approximately $6.3 billion, with around $3 billion frozen on-chain at the time of its October 30 update.
The incident nevertheless highlights a larger shift in Ethereum wallet security. Protecting a seed phrase is no longer the entire security model. As externally owned accounts become programmable through mechanisms such as EIP-7702, users also need to understand what code their wallet has authorized, what permissions that code can exercise and how long those permissions remain active.
Key Takeaways
- Binance’s latest official investigation has not identified a wallet private-key leak.
- The incident does not establish that EIP-7702 itself was exploited or that Ethereum wallets generally are vulnerable.
- EIP-7702 allows an externally owned Ethereum account to delegate execution to smart-contract code.
- A malicious or vulnerable delegate can potentially obtain extremely broad control over the delegated account.
- EIP-7702 delegation is materially different from a normal ERC-20 token approval.
- Connecting a wallet to a website does not by itself transfer control, but signing an unsafe authorization can create much greater risk.
- Ethereum wallet security is increasingly becoming a question of both key security and permission security.
What Binance Has Actually Confirmed
Separating confirmed information from early technical speculation is essential when analyzing a security incident of this size.
Binance said its initial investigation suggests that a compromised DevOps engineer’s laptop enabled an attacker to gain access to a service container and submit unauthorized withdrawal transactions. The exchange also said it had found no evidence that wallet private keys were leaked. As an immediate response, Binance temporarily suspended deposits and withdrawals, revoked the affected address authorization and worked with blockchain partners and law-enforcement organizations to freeze and trace affected assets.
That wording matters because early on-chain analysis circulated theories involving EIP-7702 authorizations. Those observations may remain relevant to understanding how an affected account behaved, but they are not equivalent to a confirmed root cause.
Until Binance publishes its detailed technical post-mortem, the safest conclusion is narrower: an authorization-related component may be relevant to the incident, while Binance’s official preliminary explanation currently centers on compromised operational infrastructure.
Binance Incident: Confirmed vs. Not Yet Confirmed
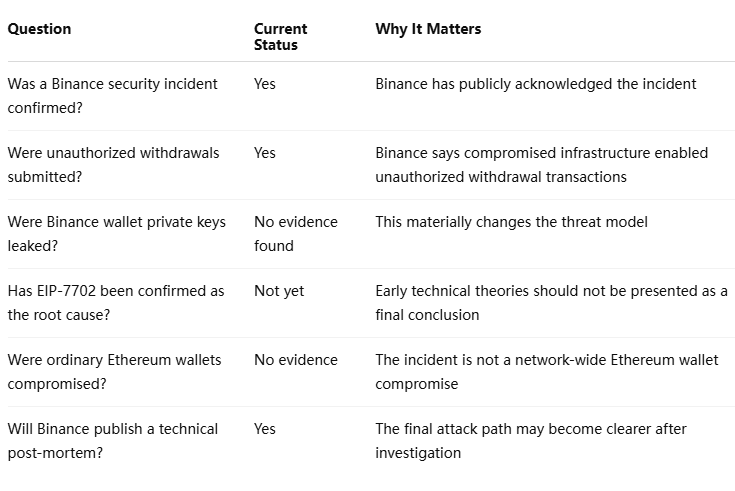
This distinction is important for Ethereum users because a compromised exchange infrastructure system and a compromised personal wallet are very different security scenarios.
Why EIP-7702 Is Relevant to Ethereum Wallet Security
EIP-7702 changes what an externally owned account, or EOA, can do.
Historically, a normal Ethereum EOA was primarily understood as an address controlled by a private key. EIP-7702 allows that account to set a delegation indicator pointing to smart-contract code. Calls to the delegated account can then execute the referenced code in the context of that account.
The feature was designed to bring smart-account capabilities to existing Ethereum accounts without requiring users to migrate their assets to entirely new wallet addresses. Potential applications include transaction batching, gas sponsorship and more granular sub-key permissions.
That creates meaningful usability improvements. A wallet could, for example, bundle an approval and a swap into one operation or allow another party to sponsor transaction fees.
But programmability also introduces another security surface.
The official EIP-7702 specification explicitly warns that code selected through an authorization can have unrestricted access to the account and should therefore be closely audited by wallet providers. It further states that poorly implemented delegate contracts can give an attacker near-complete control over a signer’s EOA.
For users, this changes the security question from:
“Does anyone have my private key?”
to:
“What has my account authorized to execute?”
That is a fundamental shift.
Ethereum Wallet Risk Is Moving From Keys to Keys Plus Permissions
The traditional wallet-security model is relatively straightforward. If the seed phrase and private key remain secret, the owner retains control of the account.
Smart-account functionality makes that model more layered.
An account may now interact through token approvals, Permit signatures, session keys, delegated smart-account logic and application-specific permissions. These mechanisms are not equivalent, and their potential impact varies significantly.
Ethereum Wallet Authorization Risk Matrix
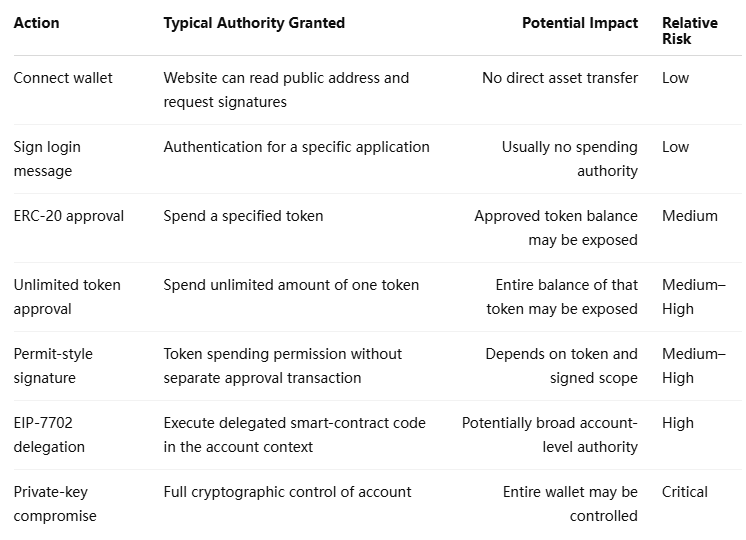
The table illustrates why users should not treat every wallet signature as equivalent.
A token approvalA token approval generally affects a particular asset. A private-key compromise affects the entire account. EIP-7702 sits much closer to the second category than the first because delegated code can control how the account itself behaves.
EIP-7702 vs. ERC-20 Approval: The Difference Matters
Many Ethereum users have already learned to check token approvals after interacting with unfamiliar decentralized applications. That remains useful, but an EIP-7702 authorization operates at a different layer.
An ERC-20 approval typically tells a token contract:
“Allow this spender to transfer up to this amount of this token.”
EIP-7702 can effectively tell the Ethereum account:
“Use this smart-contract code when executing account logic.”
That distinction dramatically changes the potential permission scope.
Figure 1 — Simplified Ethereum Authorization Layers
                           Ethereum Account
                                  │
                  ┌───────────────┴───────────────┐
                  │                               │
             Private Key                   Account Permissions
                  │                               │
          Full account control          ┌────────┴─────────┐
                  │                     │                  │
             CRITICAL RISK         Token Approval    EIP-7702 Delegation
                                        │                  │
                                 Token-specific       Account-level logic
                                    exposure             exposure
                                        │                  │
                                   MEDIUM–HIGH            HIGH
This does not mean EIP-7702 is inherently dangerous. The feature itself is infrastructure.
The risk depends on which delegate contract is authorized and how that contract is designed.
A well-audited smart-account implementation can use EIP-7702 to improve wallet security by allowing privilege de-escalation, spending limits or specialized sub-keys. A malicious delegate can produce the opposite outcome.
The technology therefore increases both the potential capability and the importance of implementation quality.
Could the Binance Hack Affect Your MetaMask or Ethereum Wallet?
There is currently no evidence that the Binance incident directly compromises MetaMask, Rabby or ordinary Ethereum wallets simply because they operate on Ethereum.
An Ethereum wallet does not inherit permissions from Binance. Binance’s hot-wallet infrastructure, exchange accounts and internal authorization systems are separate from the permissions attached to a user’s personal on-chain address.
That means holding ETH in a self-custody wallet does not create exposure to the Binance incident by itself.
What users should pay attention to is whether their own wallet has independently signed suspicious authorizations.
The relevant risk factors include interacting with phishing applications, signing unfamiliar account-delegation requests, exposing a seed phrase, installing malicious browser extensions or approving transactions through a compromised device.
This distinction matters because large security incidents often generate a secondary wave of phishing campaigns. Users searching for phrases such as “Binance hack wallet safety,” “EIP-7702 revoke,” or “check Ethereum wallet after Binance hack” may encounter fake security tools designed specifically to exploit the heightened concern.
Can Simply Connecting a Wallet Give an Attacker Control?
Normally, no.
Connecting a wallet primarily exposes the public wallet address to an application and allows that application to request signatures or transactions.
The dangerous step occurs when the user signs something that grants authority.
A malicious website may disguise such a request as a wallet verification, security upgrade, migration, token claim or account-protection procedure. If the user authorizes powerful delegated code, the risk can become materially greater than a standard wallet connection.
The official EIP-7702 specification takes an unusually strong position on this issue. It states that applications should not expect users to safely evaluate arbitrary authorization requests and places significant responsibility on wallets to closely audit delegated code.
That is an important design signal: even technically experienced users may not be able to determine the safety of an arbitrary delegation by reading a wallet popup.
A Better Model for Evaluating Ethereum Wallet Risk
Instead of asking whether a wallet is simply “safe” or “unsafe,” users can evaluate exposure through four layers.
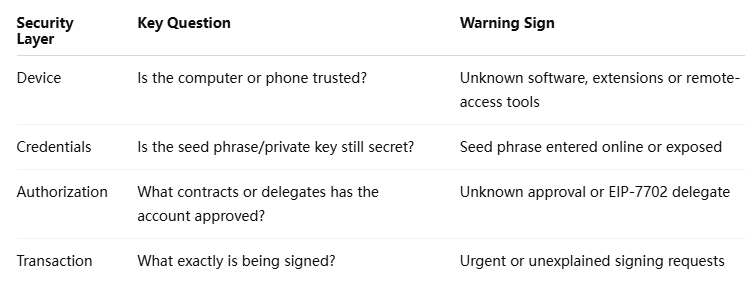
If an attacker can induce the owner to sign sufficiently powerful authorization, the key may remain cryptographically secure while the assets become operationally exposed.
That difference is likely to become increasingly important as smart accounts become more widely adopted.
What Ethereum Users Should Check After the Binance Security Incident
Users do not need to panic-migrate assets solely because Binance experienced a security incident. Moving funds under time pressure can actually increase exposure to phishing.
A more useful response is to review the state of the wallet.
Start with recent wallet activity. Look for transactions or signatures that you do not recognize, particularly interactions that occurred through links received in private messages, search advertisements, Telegram groups, Discord channels or unsolicited support conversations.
Then review token approvals. Unlimited approvals to abandoned or unfamiliar applications should receive particular attention, although token approvals alone do not reveal every account-level permission.
Users who rely on wallets supporting smart-account functionality should also check whether an unexpected delegation has been configured. The important question is not simply whether delegation exists, but which contract the account delegates to and whether the wallet provider recognizes that implementation.
Finally, check the device itself. Browser extensions, clipboard malware, remote-access tools and compromised developer environments can defeat otherwise secure wallet practices.
When Should You Move Assets to a New Ethereum Wallet?
Creating a new wallet can be appropriate when there is credible evidence that the existing wallet’s root credentials have been compromised.
Examples include a leaked seed phrase, exposed private key, confirmed malware on the signing device or unexplained account-level authorization that cannot be safely removed.
But moving assets purely because of a headline can introduce unnecessary risk.
A user who searches for an emergency wallet migration tool, connects to an unverified website and signs an unfamiliar transaction may create a security problem that did not previously exist.
The decision should therefore depend on evidence from the user’s own account rather than the size of the Binance incident.
Why EIP-7702 Could Become a Major Wallet Security Topic
Ethereum wallet architecture is gradually moving from passive key containers toward programmable accounts.
That transition could solve several long-standing user-experience problems. Transaction batching can reduce repeated signing. Gas sponsorship can allow applications to pay transaction fees. Restricted session keys can reduce the need to expose full account authority to every interaction.
Yet the same programmability makes authorization infrastructure more important.
EIP-7702 changes several assumptions that historically applied to EOAs. The specification notes, for example, that once an EOA is delegated, calls to the account may cause its balance to decrease even when the transaction did not originate directly from that account.
This matters for exchanges, wallet developers, custody providers and security monitoring systems as much as it matters for individual users.
Systems built around the assumption that “EOA equals simple private-key account” may increasingly need to identify delegated accounts and analyze the code controlling them.
The Bigger Security Lesson From the Binance Incident
The most significant lesson may ultimately have little to do with whether EIP-7702 is identified as the final technical cause of the Binance breach.
Binance’s current explanation already demonstrates that wallet security depends on an entire operational chain: employee devices, service containers, signing infrastructure, withdrawal controls, account authorizations, monitoring systems and on-chain response capabilities.
For a centralized exchange, a secure private key cannot compensate for compromised transaction infrastructure if an attacker can cause an authorized system to submit malicious withdrawals.
For an individual Ethereum user, the parallel is straightforward.
A secret seed phrase cannot protect assets from every threat if the wallet owner separately grants dangerous authority to malicious code.
Figure 2 — Modern Ethereum Wallet Attack Surface
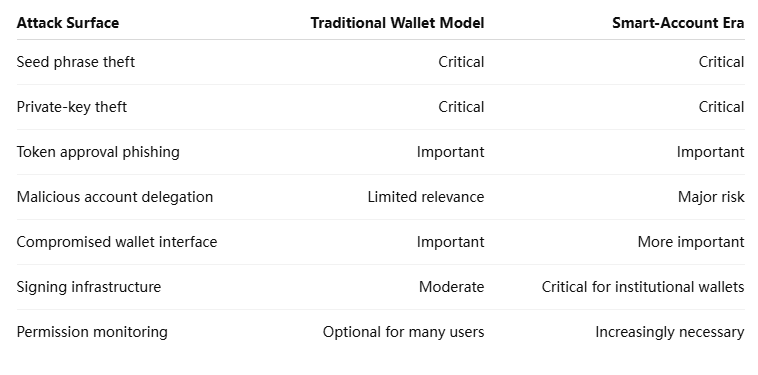
Ethereum wallet security is therefore becoming less binary.
The future security question will not simply be “Who has the key?”
It will increasingly be:
Who has the key, what has the account authorized, and what can the authorized code do?
FAQ: Binance Hack, EIP-7702 and Ethereum Wallet Safety
Does the Binance security incident mean Ethereum wallets are compromised?
No. Binance has not reported a network-wide Ethereum vulnerability. Its preliminary investigation says a compromised DevOps engineer’s laptop may have allowed access to a service container used to submit unauthorized withdrawal transactions, and Binance says it has found no evidence that wallet private keys were leaked.
Was EIP-7702 responsible for the Binance hack?
That has not been officially established. Early technical analysis discussed EIP-7702-related authorizations, but Binance’s current official statement does not identify EIP-7702 as the confirmed root cause. A detailed technical post-mortem is still expected.
What is EIP-7702?
EIP-7702 is an Ethereum protocol feature that allows an externally owned account to delegate its execution logic to smart-contract code. It enables features including batching, gas sponsorship and more advanced account functionality.
Can EIP-7702 drain an Ethereum wallet?
EIP-7702 itself does not drain wallets. However, the official specification warns that malicious or poorly implemented delegated code can obtain extremely broad control over an EOA. The security of the delegate contract is therefore critical.
Is EIP-7702 delegation the same as a token approval?
No. An ERC-20 approval generally authorizes a specific spender to transfer a particular token. EIP-7702 delegation affects how the account executes smart-contract code and can therefore have a much broader permission scope.
Does connecting MetaMask to a website expose my wallet?
Connecting a wallet alone generally does not give a website authority to transfer assets. The greater risk comes from subsequently signing malicious transactions, token approvals, Permit messages or account-level authorizations.
Should I revoke every Ethereum wallet approval after the Binance hack?
Not automatically. Users should review unknown or unnecessary permissions, but randomly connecting to third-party “revoke” websites can create additional phishing risk. Account-level delegation and ordinary ERC-20 approvals should also be evaluated separately.
Should I transfer all ETH to a new wallet?
Not solely because of the Binance incident. Migration is more appropriate when there is evidence that the user's own seed phrase, private key, device or account authorization has been compromised.
Final Analysis
The Binance security incident is an important reminder that blockchain security is moving beyond the simple distinction between “private key safe” and “private key stolen.”
Ethereum accounts are becoming programmable.
That creates a better user experience, but it also expands the authorization layer that sits between a private key and an asset transfer.
EIP-7702 is part of that evolution. It can support better smart wallets, transaction batching and more controlled account permissions. At the same time, Ethereum’s own specification makes clear that delegating to unsafe code can expose an account to extremely broad control.
For ordinary users, there is no evidence that the Binance incident requires a mass migration of Ethereum wallets. The more useful response is to understand which permissions already exist on an account, avoid emergency actions prompted by unsolicited messages and treat account-level delegation as a security-sensitive operation rather than another routine wallet popup.
For exchanges, custodians and wallet providers, the implication is broader. Security systems increasingly need to monitor not only who can sign, but also what the account has been authorized to execute.
That may ultimately be the more lasting lesson from the Binance incident.

评论
仅可选择预设评论和表情符号